Website security is more important than ever. Cyberattacks keep getting smarter. Every website faces real threats. This includes personal blogs. It also includes large eCommerce stores. Hackers can break in. They can install malware. They can steal data. They can take your site offline. One attack can hurt your reputation. It can drop your search rankings. It can cost you money too.
Many website owners focus on design. They work hard on content. But they forget web hosting security. That is a big mistake. Your hosting environment is your foundation. It keeps your website safe. It protects customer data. It secures your online business.
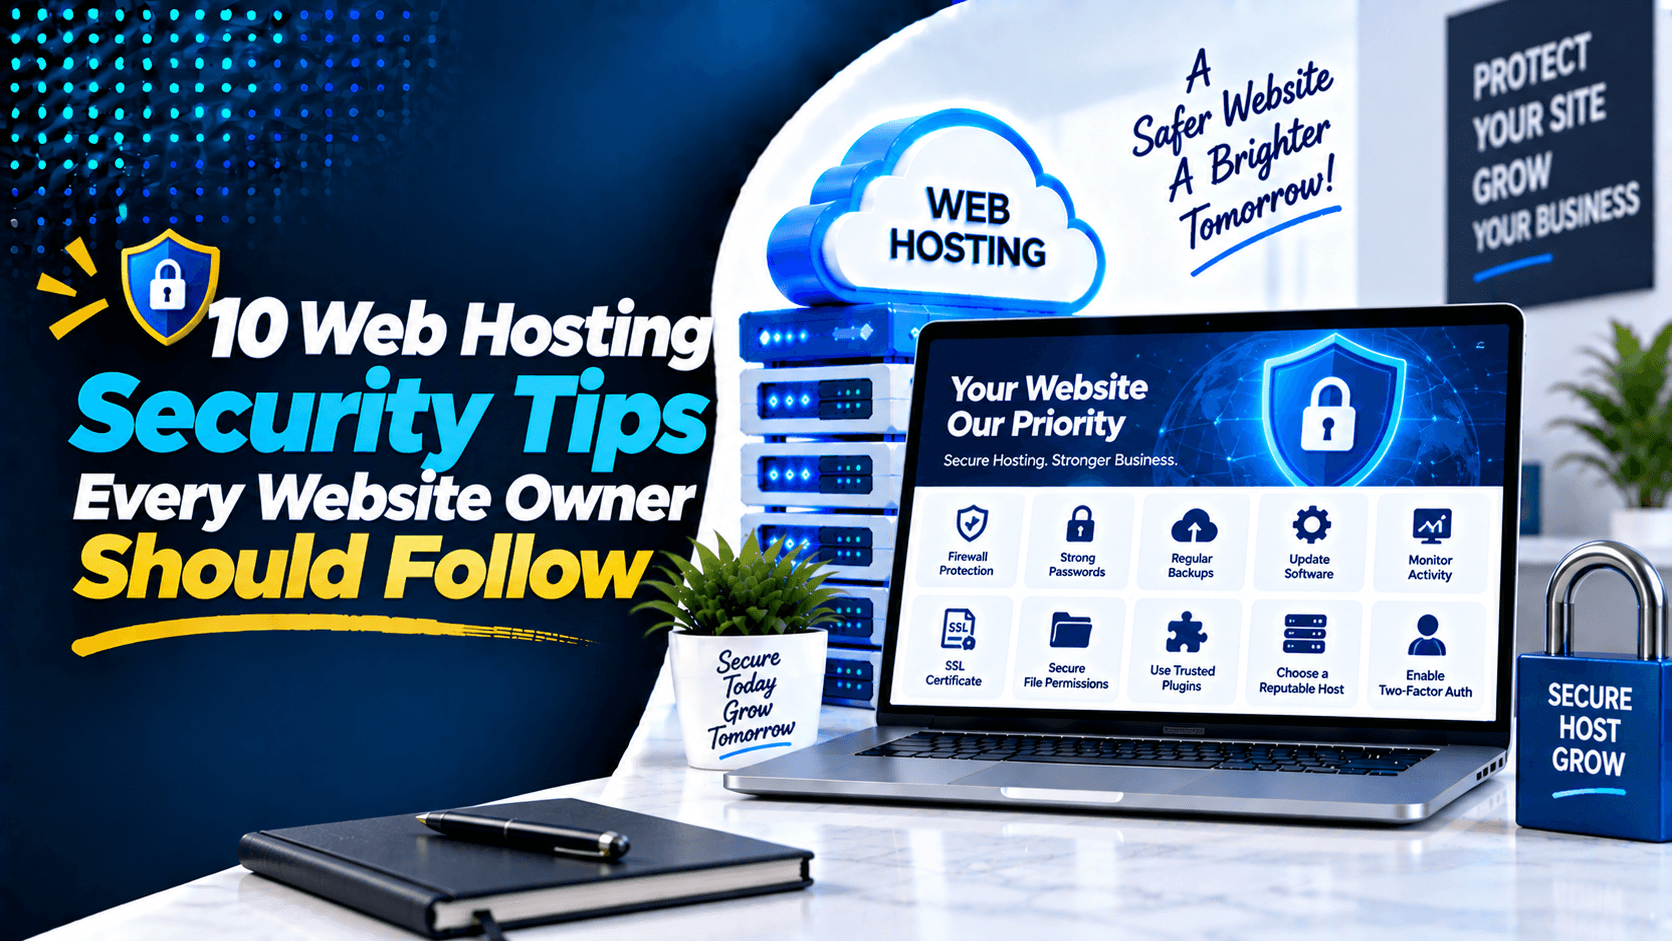
This guide shares 10 web hosting security tips. Every website owner needs them. These tips reduce security risks. They improve website performance. They help you keep customer trust.
1. Choose a Secure and Reliable Hosting Provider
Your web host is your site’s foundation. A weak foundation puts everything at risk. That is why you need a provider that puts security first. This is your most important defense.
Features to Look for in a Hosting Company
Choose a hosting provider that offers:
- Free SSL certificates
- Daily automatic backups
- Web Application Firewall (WAF)
- Malware scanning
- DDoS protection
- Automatic software updates
- 24/7 security monitoring
- Secure data centers
- Regular server patching
Security Certifications and Reputation
Before purchasing hosting, research:
- Customer reviews
- Uptime guarantees
- Security certifications
- Compliance standards
- Years in business
- Customer support quality
2. Always Use SSL Certificates
3. Keep Your Website Software Updated
Outdated software often leads to hacked websites. It is one of the most common causes.
- Update WordPress, Plugins, and Themes: Developers release updates regularly. These updates fix security holes. They patch bugs. They boost performance. They add new security features too. Never wait to install important updates.
- CMS Updates: Do you use WordPress, Joomla, Drupal, or another CMS? Always install the latest core updates. Do this as soon as they come out.
- Remove Unused Plugins and Themes: Inactive plugins and themes can have security holes too. Delete unused plugins. Remove inactive themes. Keep only what your site needs.
- Enable Automatic Updates: Automatic updates save you time. They close critical security gaps fast. Enable them for WordPress core. Turn them on for plugins. Do the same for themes. Also enable them for hosting software when possible.
Make updating a regular habit. Do not treat it as an afterthought. Your website’s safety depends on it.
4. Use Strong Passwords and Two-Factor Authentication (2FA)
Weak passwords remain one of the easiest ways for hackers to gain access.
Creating strong passwords:
- Use at least 12 characters, mixing uppercase and lowercase letters, numbers, and special symbols
- Avoid dictionary words, common phrases, or personal information (birthdays, pet names)
- Create unique passwords for every account—do not reuse passwords across services
Password managers:
- Tools like Bitwarden, 1Password, or LastPass generate, store, and autofill complex passwords securely
- You only need to remember one strong master password
- Password managers reduce the temptation to reuse weak passwords across multiple accounts
Enable 2FA for the following accounts:
- Hosting account: Prevent attackers from accessing your billing, server settings, and customer data
- cPanel: Restrict control over file management, email accounts, and databases
- WordPress admin: Block login attempts on your wp‑admin dashboard
- Email accounts: Protect sensitive communication and password reset links
5. Enable a Web Application Firewall (WAF)
A Web Application Firewall filters malicious traffic before it reaches your website.
What a WAF Does
A WAF blocks:
- SQL injection attacks
- Cross-site scripting (XSS)
- Brute-force login attempts
- Bot attacks
- Malicious requests
Protection Against Common Attacks
A WAF defends against many of the most dangerous web attacks :
- SQL injection – Preventing attackers from manipulating your database queries
- Cross-site scripting (XSS) – Blocking malicious scripts from executing in visitors’ browsers
- Cross-site request forgery (CSRF) – Unauthorized commands can be transmitted without your knowledge. The WAF prevents this from happening.
- File inclusion and remote code execution – Harmful code might try to run on your server. The WAF keeps attackers from doing this.
Many WAFs offer extra features too. These include bot protection and rate limiting. You also gain visibility into attack patterns. This helps you strengthen your overall security over time.
Cloud-Based vs Server-Based Firewalls
Cloud-Based WAF
- Filters traffic before reaching your server
- Better DDoS protection
- Faster response times
Server-Based WAF
- Installed directly on your server
- Greater customization
- May consume server resources
6. Perform Regular Website Backups
No security system is perfect. Backups ensure your website can be restored quickly if disaster strikes.
Why Backups Are Essential
Backups protect against:
- Hacking
- Malware
- Human error
- Failed updates
- Hardware failures
- Ransomware
Automatic vs manual backups
Automated backups run on a set schedule. They happen daily or weekly without any work from you. Most hosting providers offer this feature. But you should not depend on them alone.
Manual backups give you more control. You run them before making major updates. This creates a restore point in case something breaks.
Offsite backup storage
Storing backups on the same server is risky. If that server fails, you lose everything. Your live site and your backups are both gone.
Store your backups offsite instead. Use cloud storage like Google Drive or AWS S3. You can also use a remote FTP server. A dedicated backup service works well too.
Backup frequency recommendations
7. Scan for Malware Regularly
Malware can infect your website without obvious warning signs.
Signs Your Website May Be Infected
Watch for these red flags that indicate potential malware :
- Unexplained redirects to third-party sites
- Sudden slowdowns or repeated crashes
- Unauthorized admin accounts or file changes
- Hosting provider notifies about high CPU usage or outbound traffic
Malware Scanning Tools
Regular scans help detect threats early.
Popular website security tools include:
- Wordfence
- Sucuri
- Imunify360
- SiteLock
- MalCare
Automatic Malware Removal
Some hosts offer automatic malware removal for infected sites. This feature saves you time and effort. With tools like Imunify360, you can enable proactive defenses. You can also quarantine infected files directly from your hosting dashboard. This ensures a thorough cleanup process.
Server-Side Security Scanning
Many hosting providers offer:
- Real-time server scanning
- File integrity monitoring
- Threat detection
- Suspicious activity alerts
8. Limit User Access and Permissions
Limiting user access stops unauthorized people from getting into your site. It also prevents accidental changes. This is a key part of web hosting security.
- Follow the principle of least privilege: Give each user only the permissions they truly need. This practice lowers your risk. It makes compromised accounts less dangerous. It also cuts down on unwanted changes.
- Manage user roles carefully: Use roles like Administrator, Editor, Author, or Contributor. Don’t give everyone full access. Match each role to the person’s actual job.
- Remove inactive accounts right away: Former employees don’t need access. Contractors who finished work don’t need it either. Disable these accounts immediately. Also review all user accounts on a regular schedule.
- Secure your file transfers: Use SFTP instead of standard FTP. SFTP encrypts everything you send. This keeps your data safe. Limit access to specific folders when you can. You can also restrict access by IP address. Always use strong and unique passwords. For even better protection, try using SSH keys.
9. Protect Against DDoS Attacks
A DDoS attack floods your server with traffic. This makes your site slow or completely offline.
- Understand DDoS attacks: Attackers use thousands of infected computers and phones. These devices all target your server at once. This causes downtime. It also hurts your brand reputation. Knowing how they work helps you defend against them.
- Choose secure hosting: A reliable host fights DDoS attacks for you. They use traffic filtering to block bad requests. They also use rate limiting to control traffic flow. Load balancing spreads the load across servers. Attack detection catches threats early. All these features reduce the attack impact.
- Use a CDN with DDoS protection: A CDN acts like a shield. It absorbs attack traffic before it hits your server. Advanced CDN services add extra tools. These include web application firewalls and real-time threat detection. This gives you stronger protection.
- Monitor unusual traffic: Watch for sudden jumps in visitors. Look for strange connection patterns. Check your CPU, memory, and bandwidth usage. If you spot something odd, act fast. Early action can stop an attack from causing major damage. Stay alert and stay protected.
10. Monitor Website Activity and Security Logs
Regular monitoring gives you clear visibility into your site’s health. It also helps you spot attacks before they cause real harm.
Key areas to monitor:
- Server logs – Review your access logs, error logs, and FTP logs often. Look for strange patterns. Watch for repeated failed login attempts. Also check for unauthorized file access. These logs tell you who is trying to get in.
- Login monitoring – Track all admin and user logins. Set up alerts for multiple failed attempts. Also watch for logins from unfamiliar IP addresses. This helps you spot brute force attacks quickly. You can then block the attackers right away.
- Security alerts – Enable real-time notifications for suspicious activities. These include malware detection and brute force attacks. Also watch for changes to critical files. Instant alerts let you respond without delay. This keeps your site safer.
- Uptime monitoring – Use tools like UptimeRobot or Pingdom. They track your website’s availability around the clock. If your site goes down, you will know immediately. Downtime could mean a DDoS attack or a server problem. Quick alerts help you fix issues fast.
- Regular security audits – Schedule audits of your server settings, file permissions, and installed software. Do this on a regular basis. Audits help you find weaknesses before hackers do. This proactive approach stops attacks in their tracks.
A solid monitoring routine gives you full visibility into your website’s security. It helps you act quickly and keep your hosting environment safe. Stay alert. Stay protected.
Common Website Security Mistakes to Avoid
Avoid these common mistakes that leave websites vulnerable:
- Using weak or reused passwords
- Ignoring WordPress, plugin, and theme updates
- Not creating regular backups
- Installing too many unnecessary plugins
- Accessing your admin panel over unsecured public Wi-Fi
- Sharing administrator accounts with multiple users
- Ignoring security alerts or malware warnings
- Leaving default admin usernames unchanged
- Using outdated PHP versions
- Choosing hosting based only on price
Bonus Tips for Better Website Security
For stronger protection, add these practical web hosting security tips to your regular maintenance routine:
- Use Secure FTP (SFTP) instead of FTP.
- Disable directory listing to prevent unauthorized browsing.
- Protect the wp-admin area with IP restrictions or additional authentication.
- Enable bot protection to block automated attacks.
- Configure HTTP security headers such as Content Security Policy (CSP), HSTS, and X-Frame-Options.
- Perform regular vulnerability scans.
- Disable XML-RPC if not required.
- Use DNS security features where available.
- Monitor file integrity for unexpected changes.
- Keep PHP and server software updated.
Frequently Asked Questions (FAQ)
Is web hosting responsible for website security?
Hosting providers secure the server. But you handle the rest. You need strong passwords. You must update software. You manage user access. You follow best practices. Security is a team effort.
How often should I back up my website?
Back up business and eCommerce sites daily. Smaller sites can do it weekly. Always back up before updates. Also back up before big changes.
Do I need SSL for a small website?
Yes. SSL protects visitor data. It builds trust. It enables HTTPS. Google uses it for ranking. Even personal blogs benefit from SSL.
Can shared hosting be secure?
Yes. Good providers make shared hosting safe. They offer malware scanning. They include firewalls. They isolate accounts. They provide SSL and auto-updates. But high-traffic sites may need dedicated hosting. Business-critical sites may prefer cloud hosting. Both give you more control.
What’s the difference between SSL and a firewall?
SSL encrypts data between your site and visitors. A firewall blocks bad traffic before it arrives. They do different jobs. But they work well together.
How can I tell if my website has been hacked?
Watch for warning signs. Strange redirects are a red flag. Spam content appears out of nowhere. Your site slows down. Unknown admin accounts show up. Browsers show security warnings. Search traffic drops suddenly. Run regular malware scans. Monitor your logs. These steps help you catch issues early.
What is the most important web hosting security tips?
Start with a secure hosting provider. It’s your foundation. But don’t stop there. Combine several practices. Use SSL. Update regularly. Create strong passwords. Back up your data. Scan for malware. Set up firewalls. Monitor everything. That’s the best protection.
Conclusion
Website security is not a one-time task. It needs regular attention. These 10 web hosting security tips can help protect your site. They guard against hacking, malware, data breaches, and costly downtime.
Use strong passwords. Add SSL and two-factor authentication. Back up your site often. Keep software updated. Set up a firewall and DDoS protection. Pick a secure hosting provider. Watch your website for strange activity.
Do not wait for an attack. Check your website security today. Fix weak spots before they turn into big problems. Choose reliable hosting. Keep your website protected, secure, and ready to grow.
Leave a Comment